August 21, 2026
Top Data Backup Solutions for Secure Backup & Data Protection
Discover how data backup solutions protect your business from data loss. Learn practical strategies for business data backup and secure recovery in this guide.


Five recurring gaps in AI governance often let LLM data privacy fail, even when a company has a written policy. Knowing these gaps lets leaders audit their real risk instead of assuming documentation alone keeps them safe.
AI security risks are not just a technical problem—they can quickly become a business crisis. When sensitive data leaks or is misused by artificial intelligence, companies face real costs: lost trust, regulatory fines, and even lawsuits. A written AI policy might look like protection, but on its own, it often leaves surprising gaps.
A single overlooked weakness in how you manage large language models (LLMs) can expose confidential information, even if you believe your documentation is solid. Many leaders assume that having an AI governance policy means their data is safe, but the reality is more complicated.
AI systems are only as secure as the details behind their daily use. If you want to keep your business safe, you need to know where policies break down in practice—especially when it comes to LLM data privacy.
It’s easy to feel secure once you’ve put an AI policy on paper. This section looks at why that sense of safety can be misleading.
A written policy is only the starting point for protecting sensitive information. In practice, employees may not follow every rule, or they might not fully understand how those rules apply to new AI tools. This gap between policy and reality is where many data privacy failures begin.
Even the best-drafted documents can’t predict every way artificial intelligence will be used in your organization. As teams experiment with generative AI, new risks appear that the original policy never covered. When these risks go unnoticed, private business data can slip through the cracks.
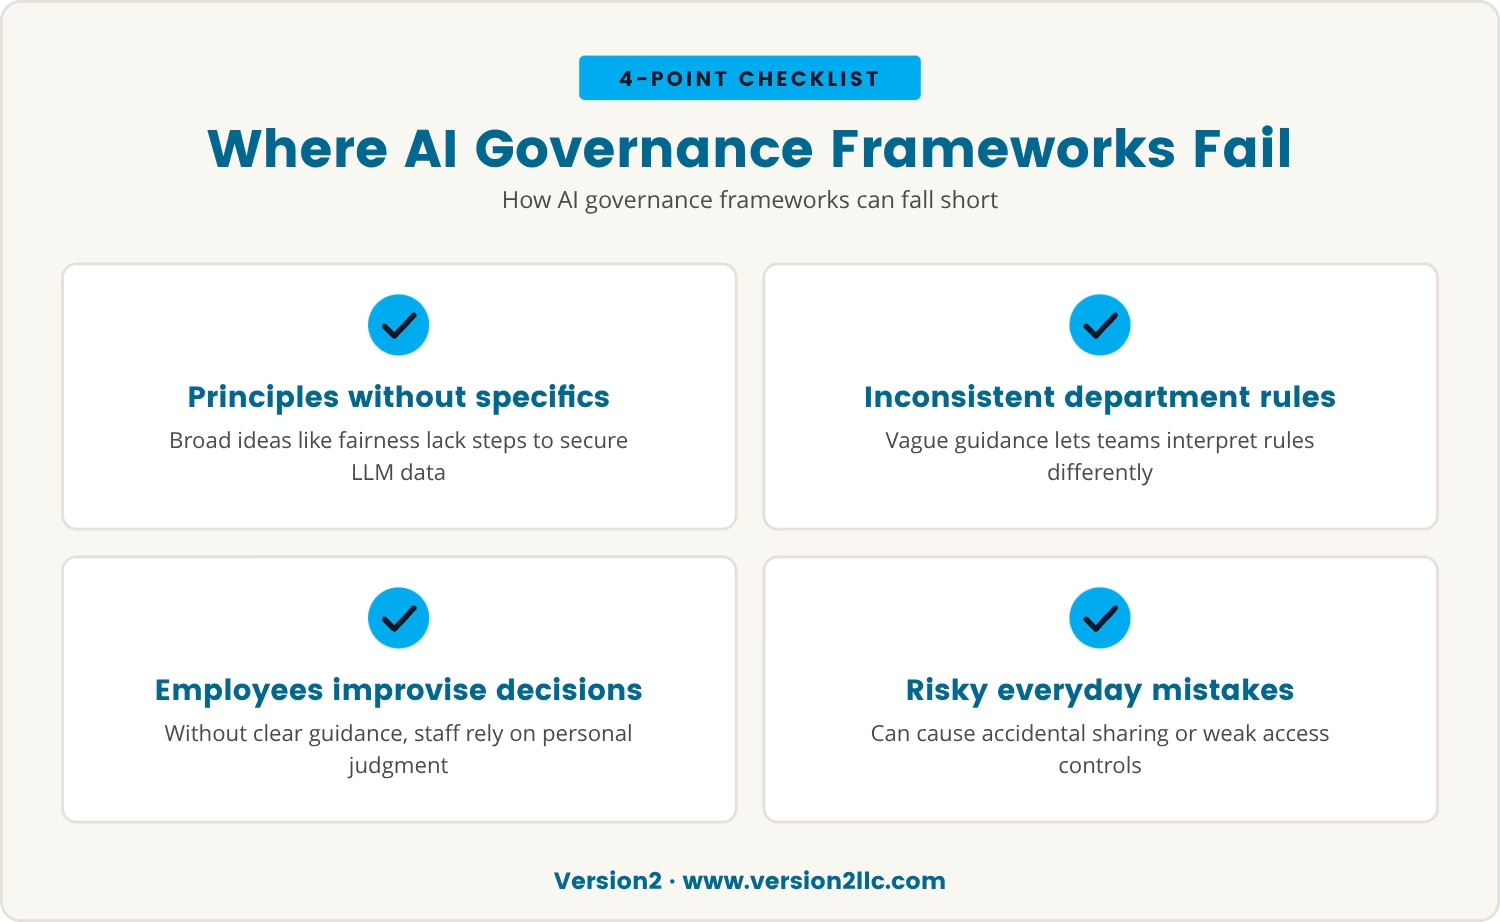
AI governance is meant to guide safe and ethical use of AI, but frameworks often miss the mark in real-world settings.
Many frameworks focus on broad principles—like fairness or transparency—without spelling out the exact steps needed to secure LLM data privacy. This leaves room for interpretation, and different departments may apply the rules in inconsistent ways.
Without clear, practical guidance, employees may rely on their own judgment when using AI tools. This can lead to accidental data sharing, weak access controls, or improper handling of sensitive inputs. Over time, these small lapses add up to major vulnerabilities.
Even with a written policy, certain weaknesses keep showing up. Here are five non-obvious gaps that often let LLM data privacy fail.
Employees sometimes use AI tools outside approved channels. These "shadow" uses can bypass official controls, making it hard to monitor what data is being shared or processed.
Policies may not clearly define what types of data are safe to enter into AI systems. Without strict input rules, sensitive information can end up in training data or outputs.
AI models often connect with outside platforms or plugins. If these integrations aren’t reviewed for security, they can become a backdoor for data leaks.
Initial training is common, but regular refreshers are rare. As AI tools evolve, employees need updated guidance to avoid new risks.
Many companies set policies but don’t actively check if they’re being followed. Without real-time monitoring or audits, violations can go unnoticed for months.
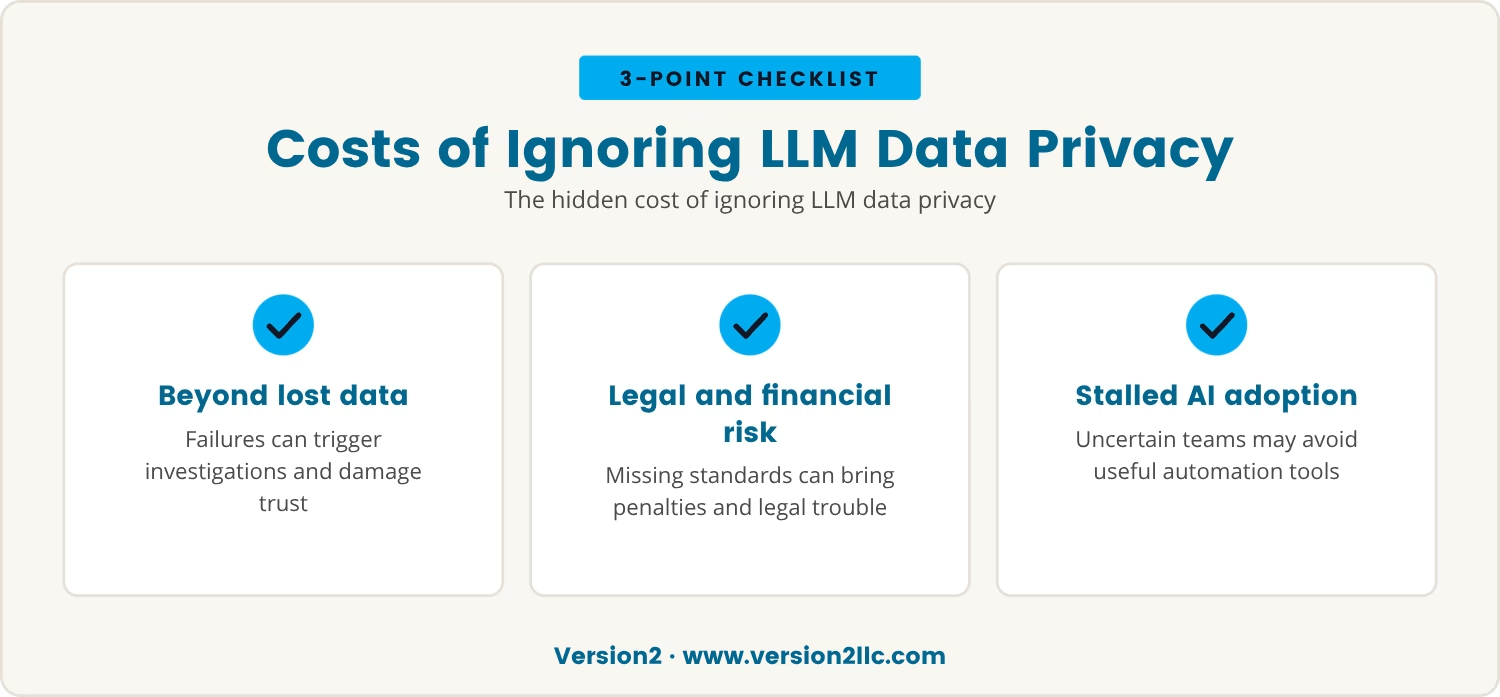
When these gaps go unaddressed, the consequences can be severe. Data privacy failures don’t just result in lost information—they can trigger regulatory investigations, damage your reputation, and erode client trust.
For businesses in Chicago, the stakes are even higher. Local regulations and industry standards may require stricter controls over how AI systems handle personal or confidential data. Failing to meet these standards can lead to legal trouble and financial penalties.
Ignoring these issues also slows down your ability to use AI safely. If your team is unsure about what’s allowed, they may avoid using helpful AI tools altogether, missing out on valuable automation and insights.
Knowing where policies fail is the first step. Here’s how you can start closing the gaps:
Each of these actions helps turn your written policy into real protection. They also make it easier to spot new vulnerabilities before they become serious problems.
Auditing isn’t just about checking boxes—it’s about finding the weak spots that policies miss. Regular reviews help you catch shadow AI use, outdated training, or risky integrations before they lead to data loss.
A strong audit process also builds confidence with clients and regulators. When you can show that your AI risk management is active and ongoing, you’re less likely to face fines or reputational harm if something does go wrong.
Ask yourself: When was the last time you reviewed how your team actually uses AI tools, not just what the policy says?
A written AI policy is a good start, but it’s not enough on its own. The real work happens in the details—tracking usage, updating training, and actively monitoring for risks.
Leaders who understand these five recurring gaps can move from assuming they’re protected to knowing they are. By turning policy into action, you protect your business, your clients, and your reputation for the long term.
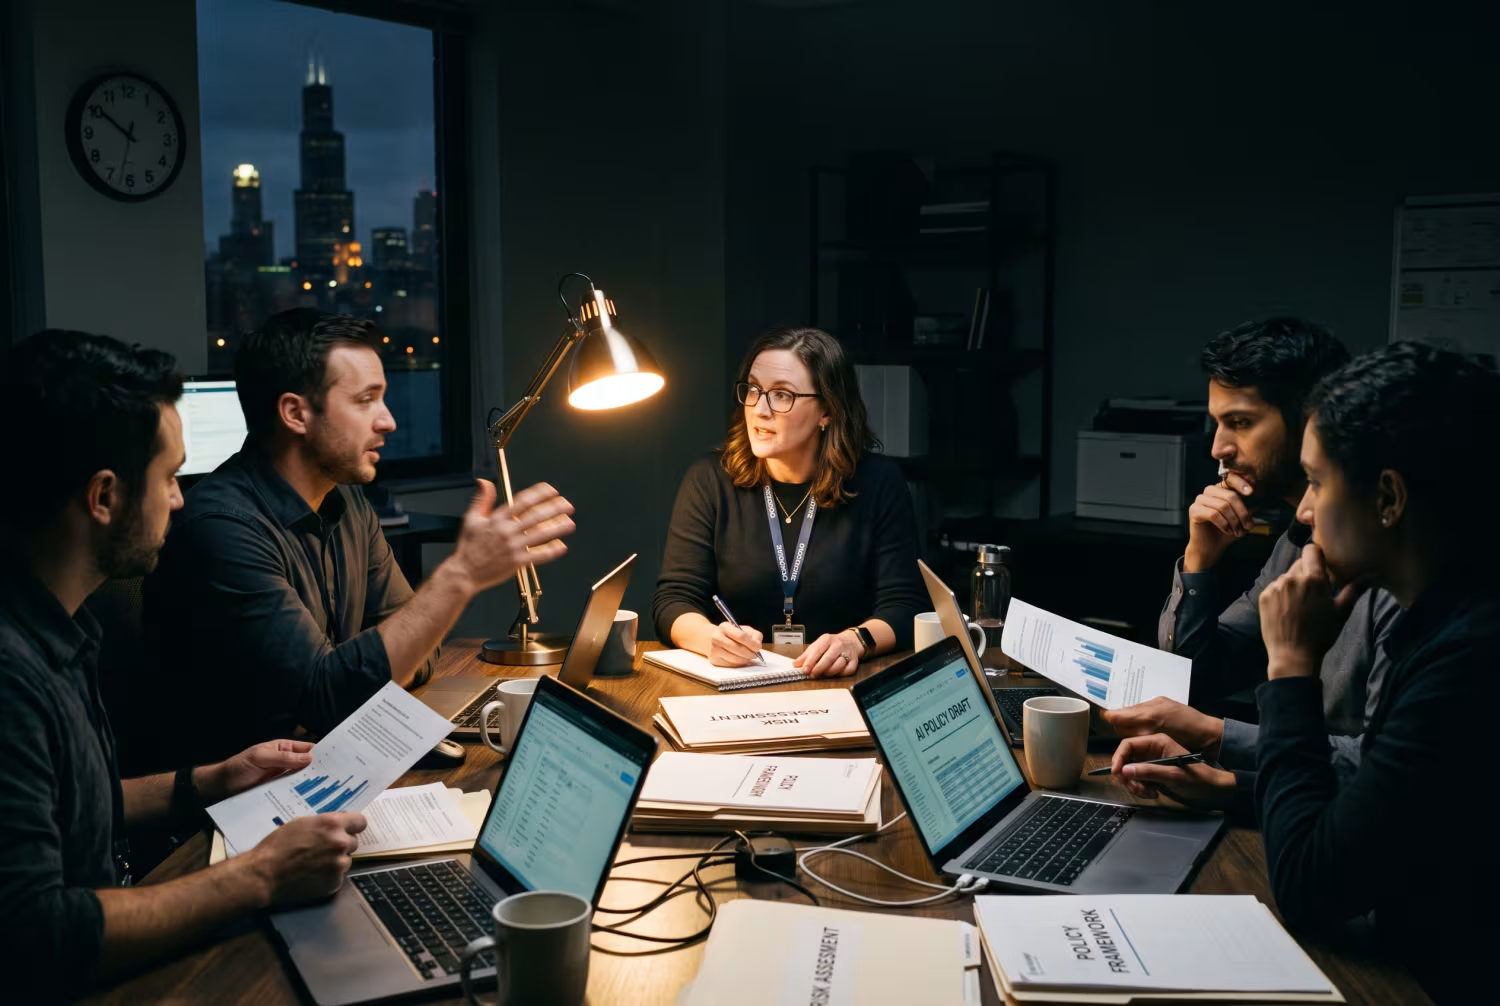
Many businesses with 10 to 100 employees have a written AI policy but still face hidden risks that documents alone can't fix. At Version2, we know how easy it is for gaps to appear between policy and daily practice.
If you want to see how we approach closing these gaps—or want to talk through your own setup—our team is ready to help you turn written rules into real security.
If you’re not satisfied in your first three months with us, we’ll refund your onboarding fee—no questions asked.
Start by mapping out all the ways your team uses AI tools, both official and unofficial. Then, use monitoring tools or regular audits to check if employees are following the rules in daily practice. Look for gaps between what’s written and what’s really happening.
If you notice employees using unapproved AI-powered apps or browser extensions, or data showing up in places it shouldn’t, you may have shadow AI use. Regularly reviewing software logs and talking with staff can help uncover these hidden risks.
Employee training should be refreshed at least once a year, and whenever you introduce new AI systems or update your policy. Ongoing reminders and short refresher sessions help keep security best practices top of mind.
Check if the integration has strong access controls, clear data handling policies, and a record of responding to security threats. Make sure you understand what data is shared and how it’s protected before connecting any new tool.
Yes, automation can make it easier to monitor AI usage, detect policy violations, and respond quickly to incidents. Automated tools can flag unusual activity and help enforce your governance framework without adding extra work for your team.
August 21, 2026
Discover how data backup solutions protect your business from data loss. Learn practical strategies for business data backup and secure recovery in this guide.
August 14, 2026
Explore how Managed IT services for small business can reduce downtime, boost security, and streamline operations with expert IT business solutions tailored for growth.
August 7, 2026
Explore cloud migration solutions, key strategies, and tools to help your business migrate seamlessly. Learn how to avoid common mistakes and ensure a smooth transition.
